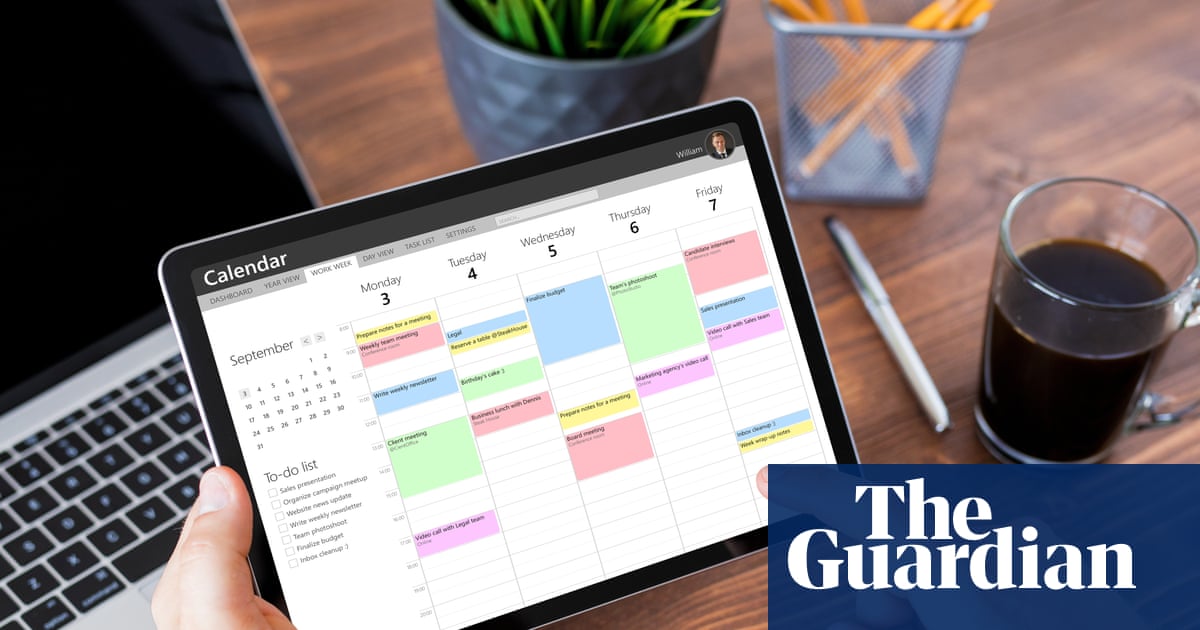
A phishing technique that plants fake appointments and payment reminders directly into victims' digital calendars is expanding rapidly, according to reporting by The Guardian. The scam relies on calendar software that can add invitations automatically, meaning a fraudulent entry can appear even when the recipient never opens the email that carried it. Targets who click through are directed to counterfeit login pages for services such as Google, Microsoft or PayPal, where they hand over their credentials.
Why it matters
The approach borrows the trust people place in their own schedules. Luke Wescott, a threat detection engineer at the security firm Sublime Security, told The Guardian that calendar phishing is still fairly new but that his company has observed what he described as exponential growth.
Wescott explained that calendar applications including Google Calendar can insert invitations on their own, without the user approving them, so scammers do not need the victim to open an email at all. He said an entry sitting alongside routine items — a dental appointment, a recurring check-in with a manager — lends the message a kind of borrowed credibility.
That shift in context is what separates this from ordinary email phishing. A message from an unfamiliar sender might be ignored or sent to spam, but a calendar notification is often treated as part of the user's own schedule rather than as an outside approach.
How the invitations reach victims
The mechanics are straightforward. Scammers send a calendar request to a work or personal email address. Whether the recipient notices it or it lands in a junk folder makes little difference, because the calendar can absorb the invitation regardless. The entry then surfaces when the person reviews their week.
Max Gannon, an intelligence analysis manager at the cybersecurity company Cofense, told The Guardian that some scammers route invitations through legitimate platforms such as Zoom. That makes the invitations appear more credible to recipients and harder for security tools to flag. Gannon said the tactic is difficult to block, and that even systems using artificial intelligence struggle with it. Filtering out invitations from those platforms, he noted, would also cut off genuine meeting requests.
The subject lines vary widely. Examples reviewed by The Guardian included fabricated meetings, alerts about voicemail messages and notices about software renewals. Wescott listed similar samples his team encounters: messages about a new voicemail, a payment receipt for $298.99, warnings about unusual PayPal activity, notices that an automatic payment will be processed within a day, and invitations to bid on contracts.
Gannon said an invitation can be dressed up to look like it came from inside the recipient's own organisation. Scammers are able to tailor the content and may insert a company logo, he said.
What happens after a click
The goal is consistent across the variations. According to Wescott, the scammers either want the target to follow a link to a fake sign-in page for Microsoft, Google or PayPal and enter a password, or to call a support number to cancel a charge that was never made.
Until someone clicks a link or places that call, no compromise has occurred. The fraudsters do not gain access to the contents of a calendar; the calendar is only the delivery route. Wescott described the underlying method as familiar phishing, distinguished by the channel used to reach the victim.
Stolen credentials are typically bundled with other people's data and sold, or used to break into a work email account. They can also help a criminal pose as a bank or another institution when contacting the victim later.
Advice from the researchers
Both analysts said the appropriate response to an unexpected calendar entry is suspicion rather than alarm. Gannon's guidance was blunt: people should treat every invitation as potentially hostile, even one that appears to come from a colleague nearby.
Wescott recommended switching off automatic acceptance. In Google Calendar, users can adjust settings so that invitations are only accepted from known senders, or only once the user has confirmed them.
He also cautioned against declining a suspicious invitation. Doing so can signal to the sender that the email address is active and monitored. Deleting the entry, or reporting it as spam or junk, is the safer option, he said.
The broader pattern fits a well-established playbook. Phishing campaigns succeed by imitating the places people already trust, and calendars have become one more surface where that trust can be exploited. Because the invitations often arrive through services that organisations rely on for legitimate work, blocking them wholesale carries its own costs.
For now, the practical defence rests with the individual: verify before clicking, and treat an unfamiliar meeting the same way as an unfamiliar email.